Service
Software Quality Assurance
Rigorous testing to ensure your software meets the highest quality standards.
Our QA team employs manual and automated testing methodologies to identify issues before your users do. From functional testing to performance and security audits.
Every app we ship goes through QA before it reaches a store review queue, because a rejected build costs days and a broken payment flow costs customers. We also run that same QA function as a standalone service for teams whose apps were built elsewhere.
Testing concentrates where failure is expensive: payment and subscription flows, real-time features that break under poor connectivity, offline sync and its conflict cases, permissions, and the platform requirements that cause store rejections. These are the paths that rarely survive a quick developer check on one device.
You get findings you can act on — reproducible steps, the device and OS it happened on, severity, and evidence — rather than a list of opinions. Automated suites then cover the regressions that must never come back.
What We Deliver
- Manual and exploratory testing
- Automated test suite development
- Regression and smoke testing
- Performance and load testing
- Cross-device and cross-browser testing
- Pre-launch QA audits
Start Your Project
Book a free scoping call or send us your project details.
Our approach
How we decide what to build with
The trade-offs behind the stack, so you can challenge them before the work starts.
Manual and exploratory testing
Scripted coverage of the critical paths, plus exploratory sessions that find what a script never would.
Automated regression suites
Automation for the flows that must not break again, so each release is verified without a full manual pass.
Real devices, not just simulators
Cross-device and cross-OS coverage, including older and low-end Android hardware where performance problems actually appear.
Store readiness
Checks against current App Store and Google Play requirements before submission, so review is a formality rather than a gamble.
Who this is for
Where this service fits
If one of these sounds like your team, we have done this work before.
Teams shipping to the App Store and Google Play
Catch the rejections before the reviewer does — permissions, privacy declarations, metadata and platform requirements.
Products built by another team
An app you inherited, with no test coverage and no confidence about what a release will break.
Apps handling money or real-time data
Payments, subscriptions, payouts, live tracking and messaging, where a silent failure is a support ticket at best.
Teams heading into a launch
A time-boxed pre-launch audit across the flows that matter most, with a prioritised fix list.
How we work
From first call to store launch
The same five steps run every engagement, whatever the service.
Discovery
Design
Build
Launch
Grow
Related Work
See It In Action
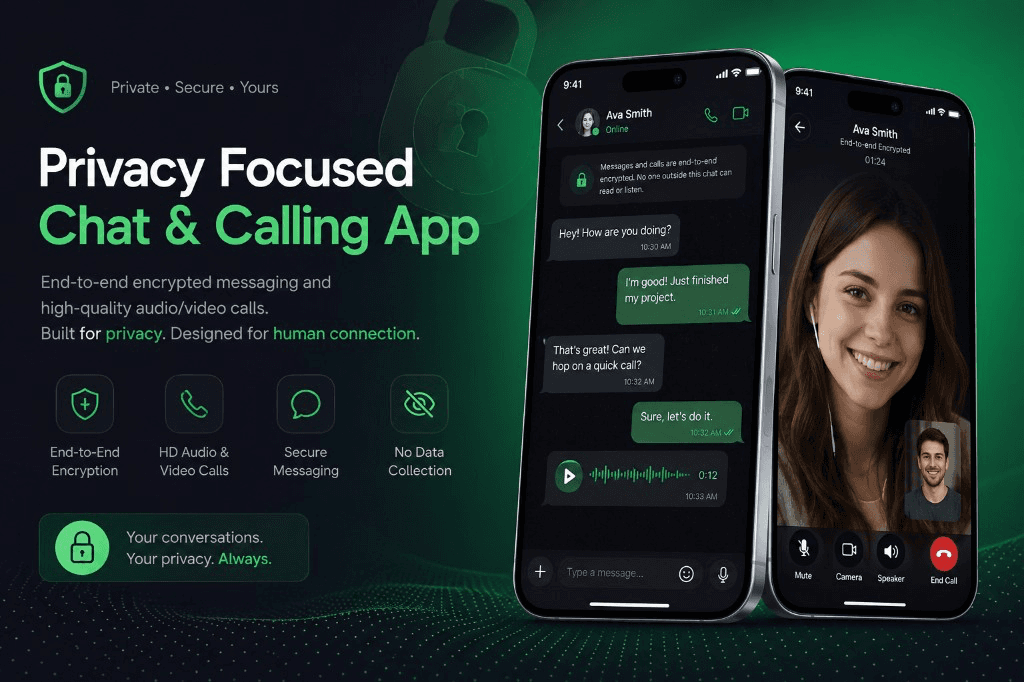
Chattick
Privacy-first encrypted messaging & calling
Launched on App Store & Google Play with full monetization
BackMe
Personal safety timer — alerts contacts if you don't check in
App Store launch with RevenueCat, ads, and marketing site
Shippacks
Dual-role package delivery — shippers and drivers
App Store and Google Play launch
FAQ
Common Questions
Can you QA an app built by another team?
Can you QA an app built by another team?
What devices do you test on?
Do you write automated tests?
Can you do a one-off pre-launch audit?
Do you test payments and subscriptions?
What do we receive?
Ready to build something remarkable?
Book a free 20-minute scoping call. We'll review your idea, share relevant case studies, and outline a realistic timeline.
Reply within 24 hours · No commitment required